Routine Maintenance or Digital Siege: America Faces Hard Questions After Unprecedented Wave of System Failures
- TDS News
- U.S.A
- November 18, 2026
By: Donovan Martin, Sr. Editor in Chief
Across the United States over the past week, the digital infrastructure that keeps commerce moving, planes flying, and intelligence flowing has buckled under a rapid succession of severe disruptions. From major financial institutions and payment networks to commercial aviation, cloud email providers, and finally the inner sanctum of American signals intelligence, independent networks have gone dark one after another. Yet in every single instance, corporate executives and federal officials have stepped forward with virtually the exact same reassuring script. According to the official line, there is nothing to see here. Each failure is being written off as an isolated technical glitch, a routine software update, or scheduled maintenance.
When the National Security Agency itself confirms that its classified internal communications network suffered a breakdown, however, the public is entitled to ask how many coincidences it takes before a pattern becomes undeniable. Either the American public is being fed a sanitized narrative designed to prevent panic while federal authorities scramble behind closed doors, or the foundational technology underpinning the United States is far more fragile and poorly maintained than anyone in power is willing to admit. Either way, calling a spade a spade requires looking closely at the timeline of events, the official explanations, and the growing chorus of cybersecurity professionals who say the government is ruling out foul play far too fast.
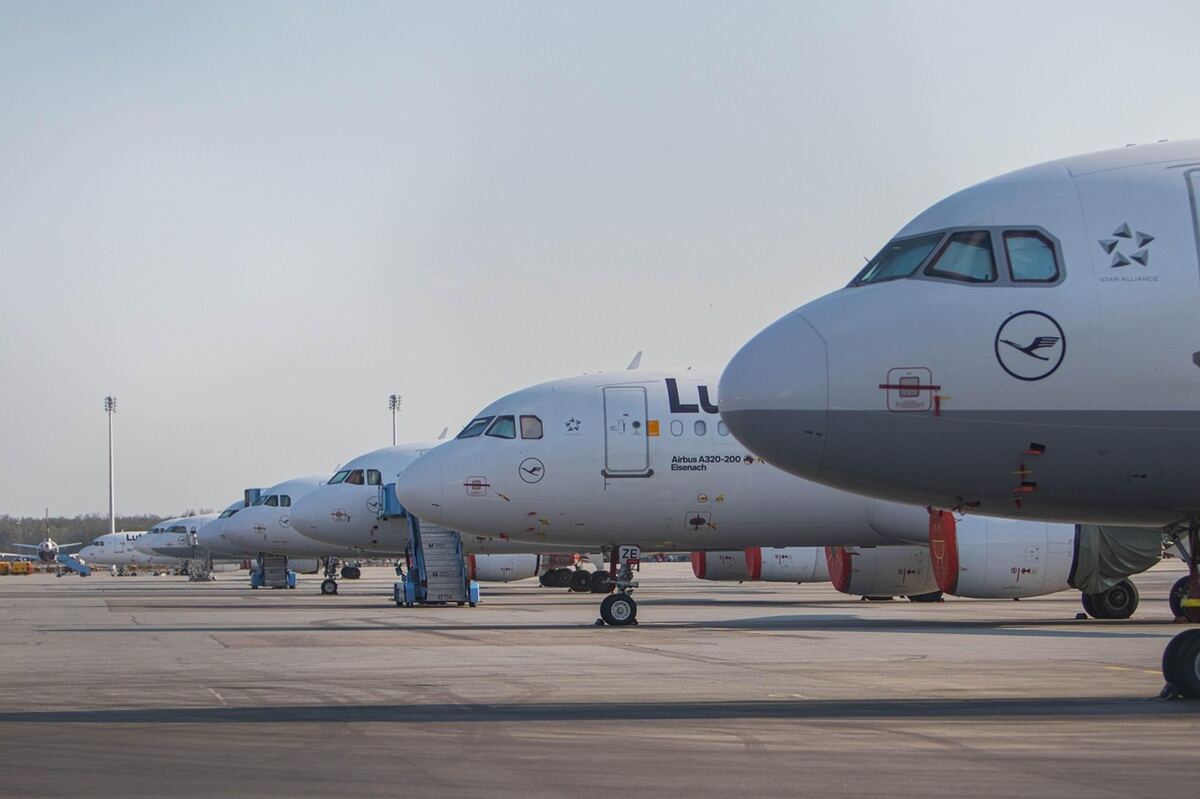
The dominoes began falling late last week when Microsoft suffered a sprawling global outage that crippled Outlook email and Teams conferencing services for millions of corporate and government workers. As businesses struggled to communicate, Microsoft attributed the collapse to a months old software bug colliding with a network capacity upgrade. Barely twenty four hours later, on Friday, November 13, the Federal Aviation Administration ordered a sweeping nationwide ground stop that lasted four hours and stranded thousands of travelers. Air traffic control facilities reported sudden system instability, and Transportation Secretary Sean Duffy later stated that the chaos stemmed from a single router failure in Arkansas rather than malicious interference.
Before travelers or markets could catch their breath, the disruptions jumped to the financial sector on Monday, November 16. Customers across the country woke up to find they could not access accounts, process card transactions, or transfer money through Zelle. The trouble began at JPMorgan Chase, the largest bank in the United States, and quickly rippled outward to ensnare customers at Bank of America and Wells Fargo. JPMorgan Chase blamed a temporary software bug and insisted the event was not a systemic issue or a cyberattack. Later that same Monday afternoon, United Airlines experienced a widespread system failure of its own that grounded departing flights across the country for ninety minutes. Apple services also registered notable disruptions during the same four day window.
Then came Tuesday afternoon, November 17, when the crisis breached the perimeter of the United States intelligence community. Reports emerged that NSANet, the highly classified internal network used by National Security Agency personnel at Fort Meade, Maryland, to share top secret intelligence, had gone offline. Internal voicemail recordings notified staff of a code yellow status, the second highest alert level governing operations at the agency headquarters, while personnel were instructed to stagger their arrivals as technicians worked to restore connectivity.
Confronted with mounting questions about how one of the premier cyber espionage and defense agencies on earth could lose its own classified communications network in the middle of a historic wave of domestic tech failures, the agency issued a carefully worded statement on Tuesday afternoon.
“The National Security Agency experienced temporary degradation during scheduled routine maintenance,” the agency said in a statement on Tuesday afternoon. “While some internal systems were affected, mission-critical capabilities remain fully operational and our ability to defend national security continues. NSA’s infrastructure is designed with multiple layers of redundancy to maintain operations during planned maintenance or unexpected events.”
For seasoned observers of national security and cybersecurity, that explanation landed with a heavy thud. The NSA does not casually take down a primary classified intelligence sharing network during active business hours in a way that triggers a facility wide code yellow alert and leaves staff unable to communicate normally, all as part of routine maintenance. Even more striking was the speed with which senior political figures and White House officials declared that a cyberattack had been completely ruled out.
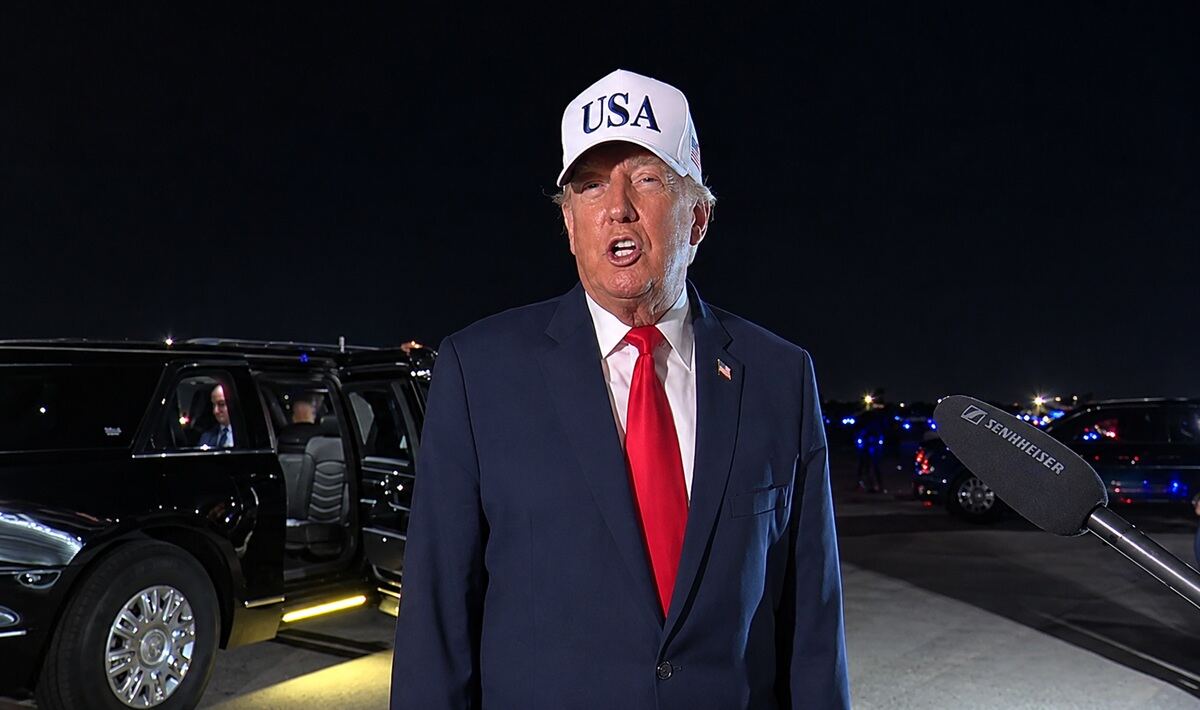
Speaking from Manila on Tuesday, President Donald Trump brushed aside the cascading failures across banks, airlines, and federal agencies, telling reporters that such breakdowns were simply a fact of life and insisting that everything was fine. White House spokesperson Lauren Bis echoed that message on television, stating flatly that officials saw no evidence of a cyberattack and that there was no crisis for Americans to worry about. Secretary of State Marco Rubio, also serving as national security adviser, admitted the string of incidents was unsettling but maintained they were entirely unrelated. Meanwhile, White House intelligence advisor Jay Clayton appeared on financial news networks to claim that institutions across the country were simply taking legacy systems offline to patch a known PHP software vulnerability, causing unexpected handoff errors when servers rebooted.
Inside the cybersecurity community and among former intelligence professionals, the administration’s certainty has been met with sharp skepticism. Investigating a suspected intrusion inside complex enterprise or government networks requires painstaking analysis of system logs, memory dumps, and network traffic. Determining with absolute confidence that a sophisticated adversary was not involved takes weeks or months, not a single afternoon.
Mike Wiacek, a veteran cybersecurity executive who previously founded Google’s Threat Analysis Group and cofounded Alphabet’s Chronicle security division before becoming chief technology officer at Stairwell, cut directly through the official talking points. While noting that outside analysts cannot prove attribution without internal forensic telemetry, Wiacek pointed out that the sequence of targets mirrors the exact playbook of a coordinated campaign.
“I can’t say for certain whether this is or isn’t a cyber attack,” Wiacek said. “But four major outages in under a week look suspiciously like what I’d expect one to look like.”
Wiacek went further, highlighting the strategic logic behind gray zone cyber operations conducted by rival nation states. If a foreign power wanted to test American resilience, sow public doubt, and inflict economic friction without crossing the threshold into open warfare, simultaneous or staggered disruptions disguised as mundane technical glitches would be the ideal weapon.
“Deniability is the point,” Wiacek explained. “And notice that no one has been physically hurt. That makes a military response hard to justify, while the economic damage and loss of public trust are real.”
Most damning of all, Wiacek called out the premature certainty coming from Washington podiums. “What concerns me most is how quickly officials ruled out an attack,” he said. “You can’t compress months of forensic work into a few hours.”
Other national security voices have raised similar alarms about the credibility gap between official assurances and observable reality. Courtney Manning, who directs an artificial intelligence and security initiative at the American Security Project in Washington, was personally caught in both the Microsoft email blackout and the nationwide aviation ground stop. Looking at the contradictory explanations offered by agencies and corporations, Manning questioned how officials could rule out a breach before identifying the root cause.
“When they say that it’s absolutely not a cyber-security incident, but we don’t actually know where these outages are coming from, definitely makes me concerned,” Manning told CBC News.
Even on Capitol Hill, lawmakers across party lines have begun pushing back against the narrative of harmless coincidence. Republican Senator Josh Hawley of Missouri mocked the notion that the simultaneous paralysis of email networks, air traffic control, major banks, and the NSA was pure chance. “If this is all a coincidence, it’s like the greatest coincidence in the history of the world,” Hawley told reporters. House Minority Leader Hakeem Jeffries formally demanded that the administration send senior officials to brief Congress on what is actually happening to the nation’s digital backbone.
To understand why so many experts and citizens refuse to accept the routine maintenance excuse at face value, it helps to examine the two competing realities facing the United States right now.
The first possibility is that the United States is experiencing a sustained, multi vector cyber campaign, or the collateral fallout of a massive zero day exploitation wave, and federal leaders are deliberately downplaying the threat. Governments routinely withhold attribution during active cyber crises to avoid tipping off adversaries about what defenders can see, to prevent bank runs or market panics, and to buy time while emergency patches are deployed across classified and private sector networks. In fact, Clayton’s admission that banks and intelligence agencies were hurriedly taking critical systems offline to patch a severe vulnerability lends weight to the idea that defenders were reacting to an urgent, active threat rather than performing calendar scheduled upkeep. When an organization pulls the plug on a live production environment in the middle of a Tuesday, that is emergency triage, not routine maintenance.
The second possibility is arguably just as troubling. Suppose every single official statement is completely true. Suppose no foreign intelligence service touched a single router in Arkansas, a single server at JPMorgan Chase, or a single switch at Fort Meade. If that is the case, it means the critical infrastructure of the world’s wealthiest superpower has become so brittle, centralized, and dependent on aging legacy code that routine software updates can routinely paralyze national air travel, freeze consumer banking, and blind the premier intelligence agency on earth.
Cynthia Kaiser, a former senior FBI cyber official who now serves as senior vice president at Halcyon’s Ransomware Research Center, pointed directly to this structural fragility. She noted that the rapid succession of breakdowns exposes how tightly coupled modern networks have become, where a single flawed update or misconfigured handoff can trigger a chain reaction across essential services. Industry reports throughout 2026 have repeatedly warned that state, federal, and private sector networks are running on decades old foundational protocols layered beneath modern cloud interfaces, creating hidden single points of failure that nobody fully maps until they break.
Yet regardless of whether the root trigger was a clandestine adversary or catastrophic technical debt, the public response from Washington has been an exercise in institutional denial. Telling millions of Americans who could not swipe their cards, check their bank balances, or board their flights that everything is fine does not restore confidence. Telling intelligence analysts locked out of NSANet during a code yellow alert that their systems simply experienced temporary degradation during scheduled maintenance insults the intelligence of everyone paying attention.
America stands at a crossroads where transparency is no longer optional. If foreign actors are probing and disrupting American financial, aviation, and defense networks under the cover of plausible deniability, hiding behind euphemisms only emboldens the attackers and leaves businesses and citizens unprepared. Conversely, if domestic digital infrastructure is collapsing under the weight of its own complexity and neglect, pretending that four major national outages in less than a week are normal growing pains guarantees that the next failure will be far worse. Until officials deliver hard forensic facts instead of reflexive dismissals, Americans have every reason to doubt the official story.
About The Author